Search News
Industry Portal
Hot Articles
How to document data center access control compliance for audits
Time
Click Count
An access control system may secure your data center, but can your records prove it during an audit? For quality and security managers, documenting data center access control compliance means connecting policies, approved access rights, visitor records, entry logs, and periodic reviews into a traceable evidence trail. A working badge reader is only one part of that story.
The difficult questions usually concern the gaps between systems: an employee transferred departments but retained server-room access; a contractor entered during an approved maintenance window, yet no escort record exists; a biometric terminal continued operating while its event feed stopped. Audit-ready documentation explains not only what should happen, but what actually happened—and how deviations were handled.
Define what the audit must prove
Before exporting logs, establish the audit boundary. Identify the facilities, secure zones, personnel groups, systems, and assessment period in scope. Distinguish between perimeter access, reception, loading areas, equipment rooms, cages, and individual racks where applicable. A building-entry record does not automatically demonstrate control over a customer’s restricted cage.
Then identify the applicable obligations. There is no single universal certificate for data center access control compliance. Your evidence package may need to support several frameworks, contractual requirements, and privacy laws.
Use the current authoritative requirements rather than a generic checklist. Not every framework requires biometrics, multi-factor authentication at every door, or an identical review frequency. Record why each safeguard is appropriate to the risk and obligation.
Build an evidence map before building a document folder
A folder containing hundreds of PDFs can still be difficult to audit. An evidence map gives each requirement a control owner, a procedure, a supporting record, and a testable outcome.
For example, “Only authorized infrastructure personnel may enter the server hall” should point to the access policy, approved role definitions, current access assignments, approval tickets, entry events, and completed access reviews. The map should also identify where the original records reside and who can retrieve them.
Include these fields in your compliance register:
- Requirement and control reference: the obligation being addressed and your internal control identifier.
- Scope and owner: affected zones, systems, personnel, and accountable role.
- Evidence source: authoritative system, report name, and retrieval method.
- Timing: control frequency, audit period, and evidence coverage.
- Retention and access: preservation period, storage location, and authorized reviewers.
- Exceptions: known gaps, compensating measures, and remediation references.
This approach also exposes unsupported claims. If a policy promises monthly access reviews but the organization performs them quarterly, either the operation or the policy needs correction—not a carefully worded audit response.
Document the complete access lifecycle
Authorization must precede activation
For each permanent or temporary credential, preserve the request, business justification, approving authority, permitted zones, activation date, and expiry where applicable. Link the credential to a unique individual rather than relying on a shared departmental identity.
An approval should demonstrate that the approver had authority over the relevant area. A line manager may confirm employment needs without being authorized to approve entry to a particularly sensitive room. Document both approvals when your procedure requires them.
Changes and departures need timestamps
Retain evidence of role changes, contract expiry, employment termination, and resulting access modifications. Compare the notification time with the actual revocation time, using the organization’s defined deadline. Include badges, mobile credentials, biometric enrollment associations, temporary passes, and controlled physical keys where used.
Review access-control administrator privileges separately. Someone who can create credentials or change door schedules may affect security without entering the facility. Preserve administrative role approvals and configuration-change records alongside physical access evidence.
Visitors require their own chain of accountability
A visitor record should connect identity verification, sponsor approval, visit purpose, permitted destination, badge assignment, arrival, departure, and escort arrangements where required. Record identity verification without automatically retaining identity-document copies; unnecessary copies increase privacy exposure.
For maintenance contractors, link the visit to a work order or change ticket. Where a colocation provider operates common-area controls and a tenant controls cage access, document that division explicitly. Provider reports support assurance, but do not replace evidence for responsibilities retained by the tenant.
Make event records reconstructable
Auditors need to follow an event across systems without guessing. A useful physical access record normally identifies the individual or resolvable credential, door or zone, timestamp and time zone, event result, and event type. Distinguish successful access, denied attempts, forced-door alarms, door-held-open alarms, and administrative overrides where the system supports them.
Document clock synchronization and monitor collection failures. Otherwise, a badge event, camera clip, and security incident may appear unrelated simply because their clocks disagree. Where controllers store events during network outages, retain evidence of local buffering and subsequent reconciliation.
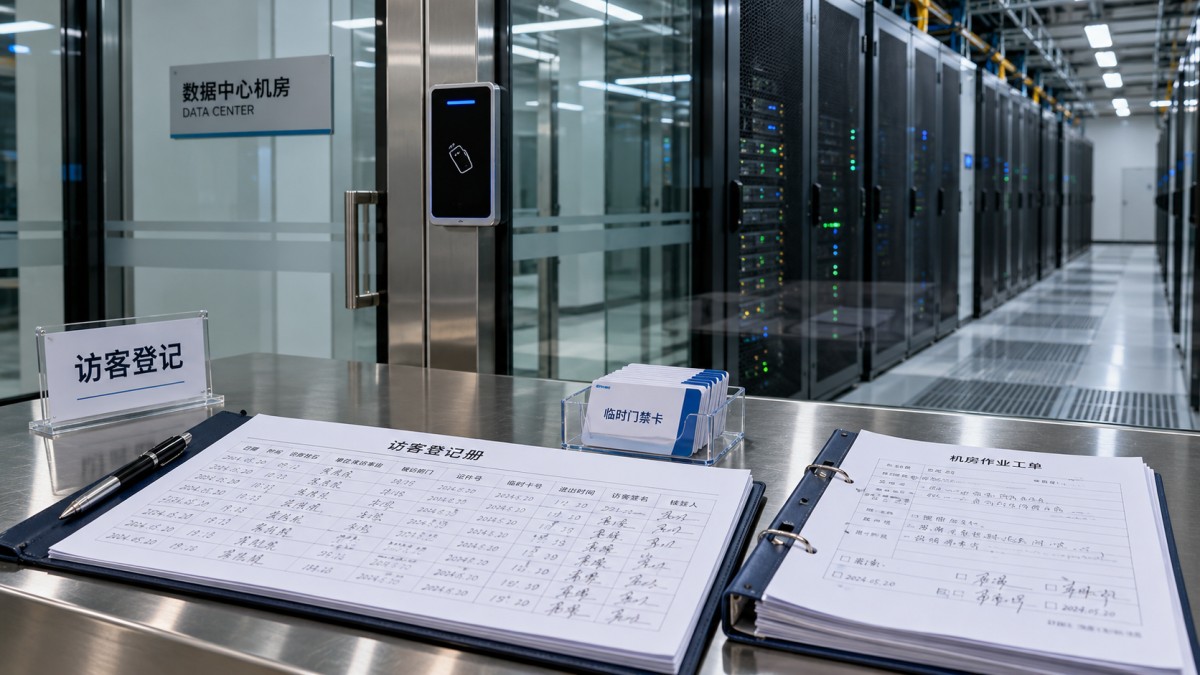
Illustrative evidence trail: a contractor’s approved work order links to a time-limited credential; that credential links to a server-room entry event; the visitor register identifies the escort; and the completed work order confirms the maintenance outcome. The identifiers need not match across systems, but their relationship must be documented.
Preserve the context of every export: source system, reporting period, extraction date, filters, time zone, and person performing the extraction. Keep original exports protected from alteration and use controlled working copies for analysis. Access restrictions, audit trails, and integrity checks can support reliability; a file hash alone does not prove the source data was complete or accurate.
Be clear about evidential limits. A successful credential event establishes that a credential was accepted, not necessarily that only its assigned holder entered. Tailgating prevention, guard observations, alarm handling, and appropriately governed video review may supply additional assurance.
Prove that reviews and exceptions lead to action
An access list is an inventory. A signed access review is evidence of a control only when it shows what was reviewed, who evaluated it, what decisions were made, and whether required changes were completed.
Set review intervals according to applicable requirements and risk. Preserve the population reviewed, reviewer authority, completion date, flagged entitlements, and associated removal or correction tickets. Reviews should consider inactive credentials, duplicate identities, expired contractors, excessive zone permissions, and privileged administrators.
For alarms and unusual entries, retain the investigation rather than merely the alert. Useful records explain the event, supporting evidence, disposition, escalation, and corrective action. Define risk-based triggers—for example, repeated denied attempts, access outside approved schedules, or a forced door—without treating every unusual event as misconduct.
Emergency access deserves a documented procedure of its own. Record the reason, authorization or emergency justification, persons involved, access duration, and post-event review. Test emergency overrides and their logging without compromising legally required emergency egress or life-safety arrangements.
Handle biometric evidence without creating a privacy problem
Biometric readers introduce additional documentation obligations; they do not automatically establish compliance. Detection accuracy, presentation-attack resistance, enrollment controls, fallback procedures, and controller integration all affect the system’s assurance.
Where GDPR applies, biometric data processed to uniquely identify a person is special-category personal data. Document both an Article 6 lawful basis and an applicable Article 9 condition. Employee consent can be problematic because the employment relationship may prevent it from being freely given. Assess relevant national law rather than assuming consent resolves the issue.
Maintain a data-flow record covering enrollment, template creation, storage, matching, transmission, vendor access, and deletion. Establish whether processing occurs on the device, on premises, or in a cloud service. Edge processing may reduce some exposure, but it does not remove privacy responsibilities.
Your supporting records should address:
- Necessity and proportionality compared with less intrusive access methods.
- A data protection impact assessment where legally required, with documented risk treatment.
- Privacy notices, processor agreements, and international-transfer safeguards where applicable.
- Encryption, template access restrictions, deletion procedures, and verified offboarding.
- A suitable alternative process for individuals who cannot use the biometric system.
Audit evidence should normally demonstrate these controls without exposing raw biometric samples or reusable templates. Keep operational access-event records separate from biometric reference data, and provide redacted or pseudonymized material where it satisfies the audit objective.
Set retention by record type—not by storage capacity
“Keep everything indefinitely” is neither a sound audit strategy nor a privacy-friendly default. Establish a retention schedule for access events, visitor records, approvals, review records, video, biometric templates, and incident files. Consider legal requirements, contractual obligations, audit coverage, investigation needs, and data minimization.
Requirements can differ even within one framework. For example, PCI DSS v4.0.1 requires applicable visitor logs to be retained for at least three months unless otherwise restricted by law. Do not assume that this period applies to every physical security record or satisfies every other obligation.
Document deletion, backup treatment, legal holds, and approved exceptions. Ensure records needed for an upcoming assessment will not expire before sampling begins. Retention settings should be tested against actual retrieval results, not accepted solely because a configuration screen displays the intended value.
Run a mock audit using real samples
Before the assessment, select a new employee, a transferred employee, a terminated contractor, a visitor, an emergency entry, and a denied-access incident where those events occurred. Trace each from authorization through operation to review or closure.
Also verify population completeness: reconcile active credentials against personnel and contractor records, and compare the door inventory with monitored event sources. A well-documented sample cannot compensate for an entire unmonitored entrance.
Where evidence is missing, record the limitation honestly. Do not backdate approvals or recreate records as though they were contemporaneous. Open a corrective action, assess exposure, apply interim safeguards, and preserve proof that the revised process works.
The strongest data center access control compliance package answers four questions consistently: who was allowed in, why they were allowed in, what actually occurred, and what happened when expectations were not met. When those answers remain connected throughout the year, audit preparation becomes verification rather than reconstruction.
Recommended News