Search News
Industry Portal
Hot Articles
UK Publishes Draft Data-Sharing Rules for Digital Verification With Biometric Safeguards
Time
Click Count
The UK government has published draft rules governing the sharing of personal data with digital identity providers, including safeguards for biometric privacy. The event date is not specified in the supplied information. The proposal sets out how public bodies would share personal data and seeks to establish a compliance framework for digital verification services. From an industry perspective, it could affect how identity providers, technology suppliers and service buyers assess data access, privacy protection and delivery requirements.
Draft framework addresses public-sector data sharing and biometric privacy
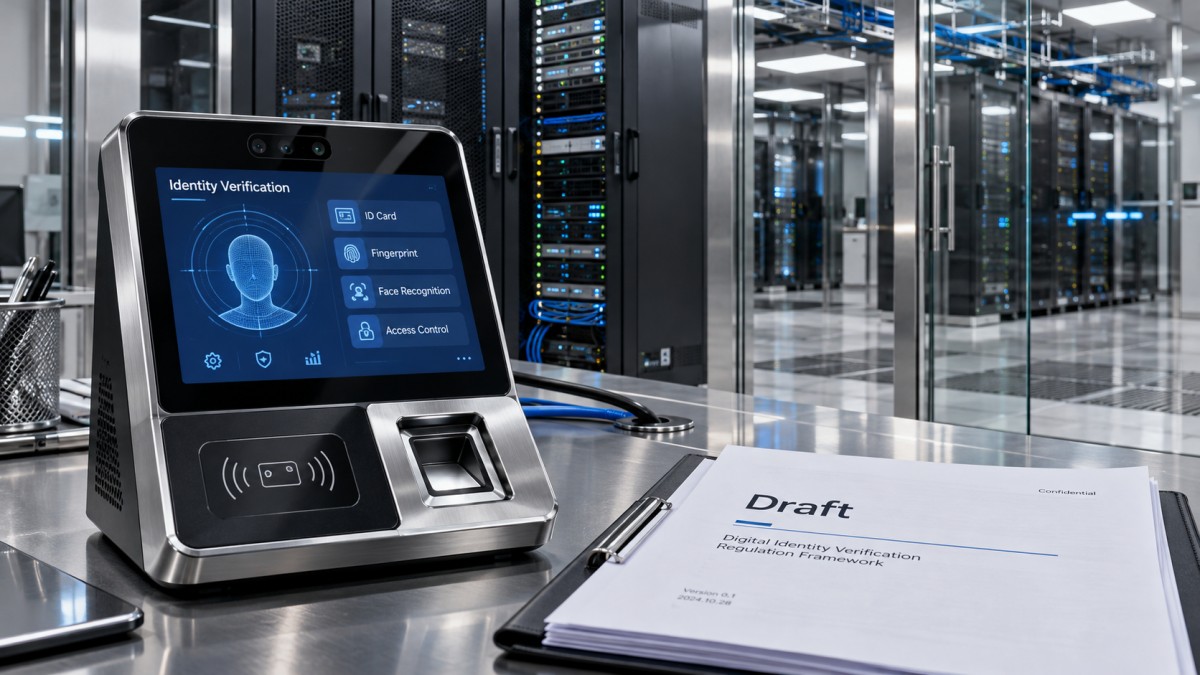
The published draft details how public bodies would share personal data with digital identity providers. It specifically includes safeguards intended to protect biometric privacy within the proposed framework for digital verification services.
The stated purpose is to address changes in government regulation and establish a compliance framework for these services. The supplied information describes draft rules; it does not specify a publication date, an implementation timetable or detailed operational requirements.
Data-sharing arrangements could shape service delivery decisions
Identity providers may need to reassess their data workflows
Analysis suggests that digital identity providers are the most directly exposed business participants because the draft concerns their receipt of personal data from public bodies. Depending on the eventual requirements, providers may need to assess how their services obtain, process and protect that information. The practical question is whether existing workflows can support the proposed framework and what supporting documentation may be needed.
Biometric suppliers could face closer scrutiny during procurement
For suppliers whose technology handles biometric information, the explicit inclusion of privacy safeguards may influence customer assessments of product suitability. From an industry perspective, buyers could seek clearer explanations of how biometric data is handled and protected. The supplied information does not establish a new testing or certification requirement, so any such procurement response remains a possibility rather than a confirmed obligation.
Public bodies and service buyers may revisit delivery assumptions
Analysis suggests that public bodies planning data-sharing arrangements, and organisations procuring services that depend on those arrangements, may need to examine responsibilities at the point where data passes between participants. If final requirements affect system design or supporting evidence, integration work and acceptance criteria could also require review. No resulting change to costs, procurement schedules or delivery periods is confirmed in the supplied information.
Preparation should focus on data flows and supporting evidence
Map the services that depend on public-sector information
As a preparatory measure, providers could identify which digital verification services depend on personal data supplied by public bodies. Mapping the relevant data flows and participating organisations would help establish where the draft may be relevant. This is an analytical recommendation, not a requirement confirmed by the supplied summary.
Review how biometric privacy is documented
Businesses handling biometric information could assess whether their technical and service documentation clearly explains the associated privacy protections. Analysis suggests that this would help them compare existing arrangements with any detailed safeguards subsequently confirmed. The available information does not establish specific controls, retention periods or evidence formats, so businesses should verify those points before treating them as compliance requirements.
Check procurement and integration assumptions
Service buyers and integration teams could review whether specifications and supplier discussions adequately address personal-data sharing and biometric privacy. Where a project depends on public-sector data access, an assessment of unresolved requirements may help inform procurement and delivery planning. Any contractual or technical changes should be based on verified rule details rather than assumptions about the draft.
Track the draft's status before committing to changes
Businesses could monitor subsequent official material for clarification of scope, responsibilities and implementation arrangements. These details would help determine whether a service requires technical changes, revised documentation or further supplier review. The supplied information does not confirm when any such changes would become necessary.
Publication signals regulatory direction, while execution remains uncertain
At this stage, it is more appropriate to understand the announcement as a regulatory development requiring assessment than as evidence that a complete operational regime is already in force. The draft's inclusion of biometric privacy indicates that protection of this information forms part of the proposed approach to digital verification.
As an editorial assessment, the most consequential follow-up would be clarification of how the proposed safeguards apply to actual data-sharing arrangements. The final wording, implementation arrangements and responses from affected organisations could influence the extent of any service redesign or procurement adjustment. The supplied information does not establish those outcomes.
A basis for targeted compliance review
From an industry perspective, the draft gives digital identity providers and their partners a reason to review the connection between public-sector data access, biometric privacy and service delivery. A proportionate response would be to identify potentially affected workflows, assess available documentation and track verified requirements as they develop. The current information supports preparation and continued monitoring; it does not establish a mandatory implementation deadline or a confirmed commercial impact.
Evidence basis and details requiring verification
This article is based solely on the news title, event-time information and event summary supplied by the user. The supplied material does not specify the event date or provide a specific official source link. The draft text and any subsequent government publications therefore remain subject to continued verification.
The discussion of potential business effects and preparatory actions is analysis derived from that limited information. Further assessment should examine official clarification of the rules, implementation arrangements, any resulting changes to procurement documents, and feedback from service providers and participating public bodies.
Recommended News