Search News
Industry Portal
Hot Articles
Google AI Glasses Raise Questions About Biometric Privacy Enforcement
Time
Click Count
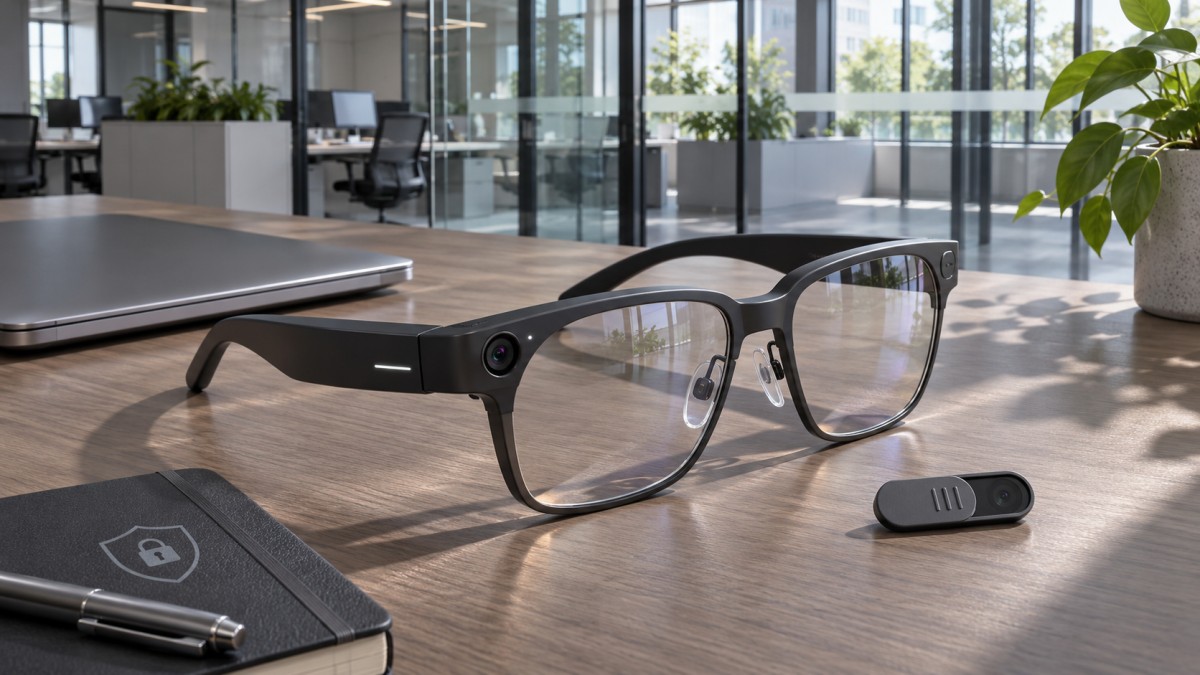
Google’s entry into the AI smart glasses market is drawing attention to a question that goes beyond the wording of its privacy rules: how effectively can those rules be enforced? According to Biometric Update, the company has introduced biometric privacy protections intended to address concerns associated with Meta’s smart glasses. Android XR platform policies explicitly prohibit facial recognition, biometric identification and real-time identification of bystanders.
Industry analysis cited in the report nevertheless raises concerns about potential gaps in the enforcement of those rules for third-party applications and in the editing of privacy-sensitive data. The distinction matters because a prohibition sets a clear boundary, while its practical effect depends on how that boundary is applied across the platform.
Why enforcement is central to the privacy promise
The policy addresses a particularly sensitive feature of AI glasses: the possibility that people near a wearer could be identified. Its explicit restrictions make biometric identification and real-time bystander identification central to the platform’s stated privacy approach.
For consumers and bystanders, however, the value of those restrictions depends on more than their presence in a policy. If third-party applications can operate in ways that evade enforcement, the protection experienced in practice could differ from the protection described in the rules. The reported concerns therefore focus on the connection between the platform’s stated prohibitions and the behavior of applications that use it.
The same distinction applies to privacy-sensitive data editing. Questions about how such data is handled relate to whether protections remain effective beyond the initial restriction on identification. The reported concern does not establish that a particular application has violated the policy or that a specific privacy incident has occurred. It does point to an area where the practical operation of the safeguards deserves attention.
What third-party applications bring into focus
Google’s policy establishes a platform-wide standard, but third-party applications are a separate point of scrutiny because their behavior determines how users encounter the platform’s capabilities. The immediate issue is whether prohibited identification functions can be consistently prevented across those applications.
For application developers, the explicit bans define activities that the policy rules out. Questions remain around how the restrictions are enforced in practice and how privacy-sensitive data editing is addressed. Those details would affect how developers assess their responsibilities and how confidently users can understand the protections available to them.
For people considering AI glasses, the distinction is also practical. A platform policy can communicate what applications are not permitted to do, but assessing its effectiveness requires evidence about how those restrictions work in use. Bystanders have a related interest because the policy explicitly addresses their real-time identification, even when they are not the people wearing the device.
What to watch next
The clearest issue for further scrutiny is whether public information explains how Android XR’s prohibitions are applied to third-party applications and how privacy-sensitive data editing is governed. Details about enforcement would help clarify the relationship between the policy’s stated boundaries and the concerns identified in the industry analysis.
At present, the policy demonstrates that Google has explicitly addressed biometric identification and bystander privacy. The broader effectiveness of those protections rests on their implementation and enforcement—questions that cannot be settled by the policy wording alone.
Recommended News