Search News
Industry Portal
Hot Articles
Cloudflare and Tools for Humanity Propose AI Agent Identity Framework
Time
Click Count
Cloudflare and Tools for Humanity, associated with World, have proposed an identity and accountability framework for AI agents acting on behalf of users. The event date was not specified in the supplied information. The proposal introduces tiered user identification and reputation mechanisms, making it relevant to website operators, cloud security providers and suppliers of biometric access controls that may need to assess how agent access is verified.
Identity and accountability for user-directed agents
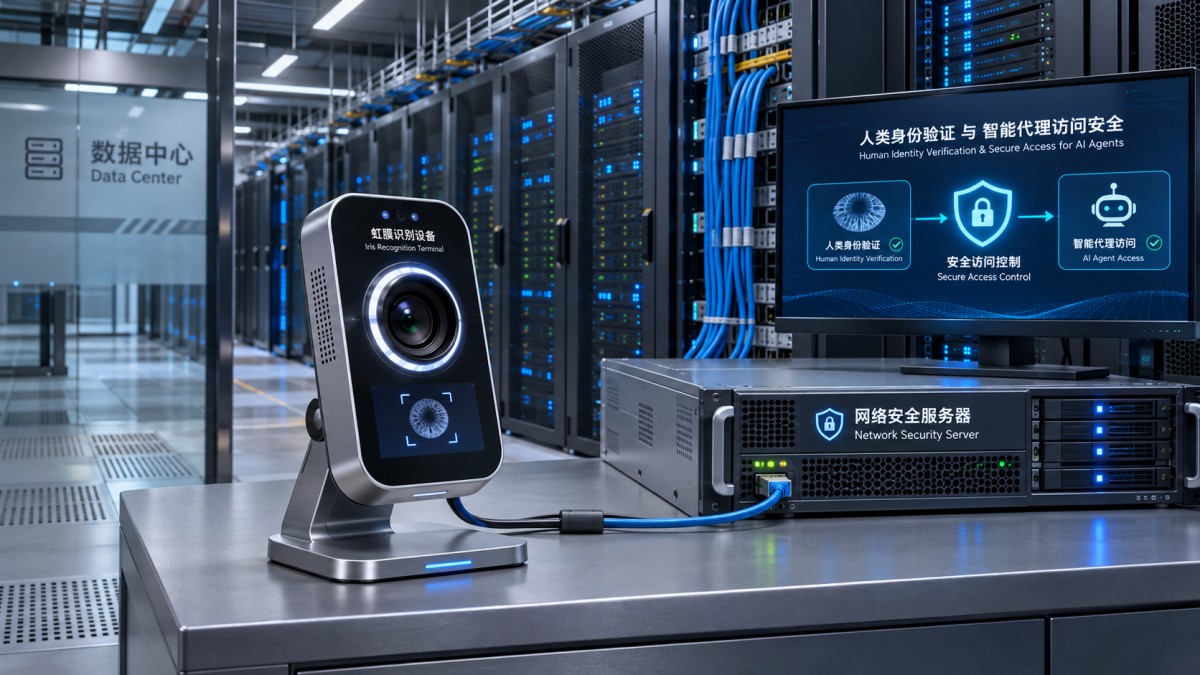
The proposed framework is intended to help websites and cloud security gateways verify the legitimacy of AI agents acting for users. It introduces tiered user identification and a reputation mechanism, and combines these with World’s iris biometric technology to confirm the human operator.
Cloudflare and Tools for Humanity present the framework in the context of AI agent access, digital identity and cloud security infrastructure. The supplied information does not specify an event date or implementation details.
Where agent verification could affect delivery
Website and cloud security operators
From an industry perspective, operators may need to consider how a site or gateway distinguishes a legitimate user-directed agent from other automated access. If the proposed approach is adopted, identity tiers and reputation information could become relevant to access decisions and to the technical specifications used when procuring or updating security services. The proposal alone does not establish a mandatory access rule.
Biometric device suppliers and integrators
Analysis suggests that suppliers of biometric access equipment and system integrators could face questions about how human verification connects to agent access controls. Procurement and delivery discussions may involve interoperability, documentation and the handling of biometric information. The supplied information does not establish device certification criteria or a required integration method.
Buyers of digital identity and security services
Organizations purchasing these services may need to assess whether a proposed solution can support their intended agent workflows and how responsibilities are allocated among providers. Any effect on supplier selection, contracting or delivery schedules remains a possibility to evaluate as implementation details emerge.
What to examine before specifying a solution
Verify the framework’s status and scope
Businesses can monitor further statements from the parties involved and check whether the proposal develops into a published specification or is adopted in procurement documents. They should distinguish a proposed framework from a binding standard, regulation or certification requirement.
Review identity and reputation details
Potential users can seek clarification on how identity tiers are defined, how reputation is assessed and what information a website or gateway would receive. These details could influence access policies and supplier evaluations, but they are not specified in the supplied information.
Assess biometric integration and documentation
Buyers and integrators can ask suppliers how iris-based human verification would connect to an AI agent’s access request, what technical documentation would be available and how the solution would handle biometric information. They can also review applicable privacy and security obligations for their own deployments; no particular legal requirement is identified in the supplied information.
Check procurement and delivery assumptions
Before incorporating the approach into a purchase or project plan, organizations can ask whether suppliers support the relevant interfaces, what validation evidence they can provide and whether integration would affect delivery. Any certification or testing expectations should be checked against later published requirements or the relevant procurement documents.
Proposal status leaves adoption questions open
Editorial analysis suggests that this development is best treated as a proposed approach and a signal for the market to watch. The supplied information does not confirm that it has been adopted as an industry standard, made mandatory by a regulator or implemented across security products.
Future assessment may depend on the availability of technical specifications, the treatment of biometric information, adoption by website and gateway operators, and feedback from suppliers and buyers. Changes in procurement language or certification criteria would also warrant review if they emerge.
Preparing for possible changes to agent access
The proposal links verification of a human operator with accountability for AI agents, potentially influencing how digital identity and cloud security solutions are specified. For now, the practical response is to monitor the framework’s development and assess its relevance to individual access, procurement and integration decisions without assuming that a formal requirement is already in force.
Basis for this report and further verification
This article is based on the supplied news title, event-time information and event summary. No specific official source link was provided in the input, so the details require continued verification. Relevant material to monitor may include official announcements, any published specifications, changes to procurement documents, implementation information and industry feedback.
Recommended News